How to Harden WordPress Security Without Breaking Your Site (Developer Playbook)
A developer playbook for hardening WordPress security: server lockdown, XML-RPC and REST API rules, database isolation, Cloudflare WAF, and a hardening checklist.
A developer playbook for hardening WordPress security: server lockdown, XML-RPC and REST API rules, database isolation, Cloudflare WAF, and a hardening checklist.
Installing an SSL certificate and forcing HTTPS on a WordPress site. WordPress SSL means your site serves every page over HTTPS with a valid certificate installed. Most hosts issue a free certificate automatically; if a page still shows “Not Secure” or a mixed content warning, the fix is usually the WordPress Address (URL) and Site […]
GEENXT tracks current WooCommerce security vulnerabilities and advisories so store owners know what to check and patch each month. WooCommerce security news changes monthly as new vulnerabilities and advisories surface across the plugin ecosystem built on WordPress. This page tracks each confirmed WooCommerce vulnerability as it is disclosed and applies one reusable response every time: […]
A practical recovery runbook for hacked WordPress sites: contain damage, preserve evidence, clean malware, restore safely, and prevent repeat compromise.
A practical WordPress security checklist for small businesses covering updates, logins, roles, hosting, HTTPS, backups, monitoring, hardening, vendors, and incident response.
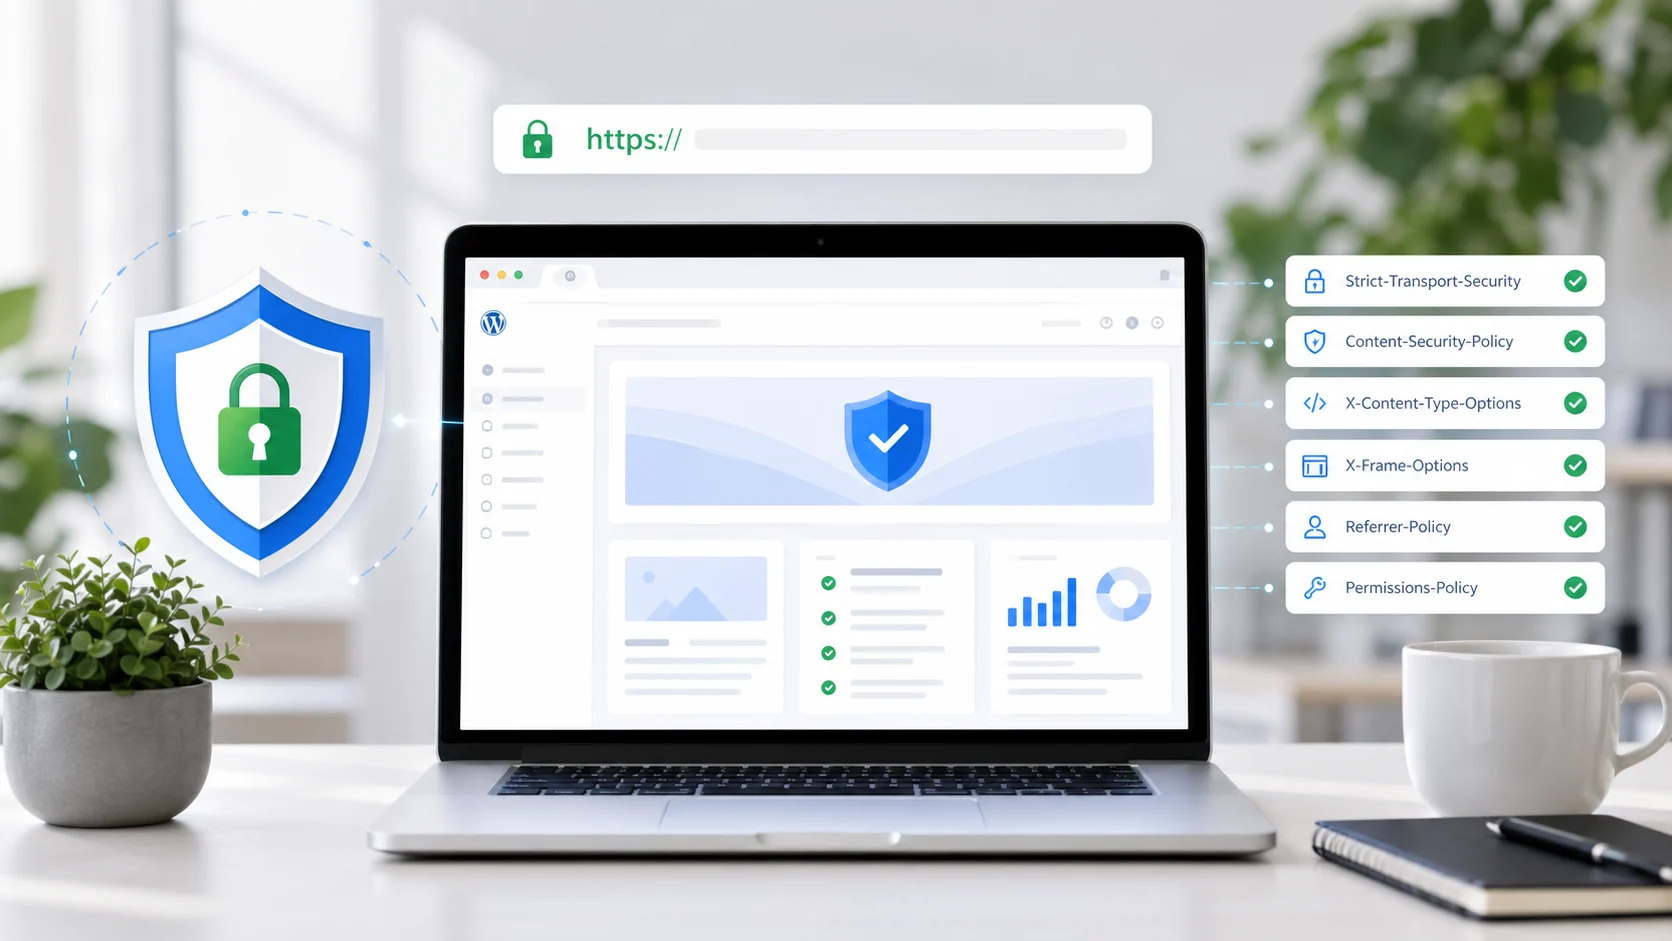
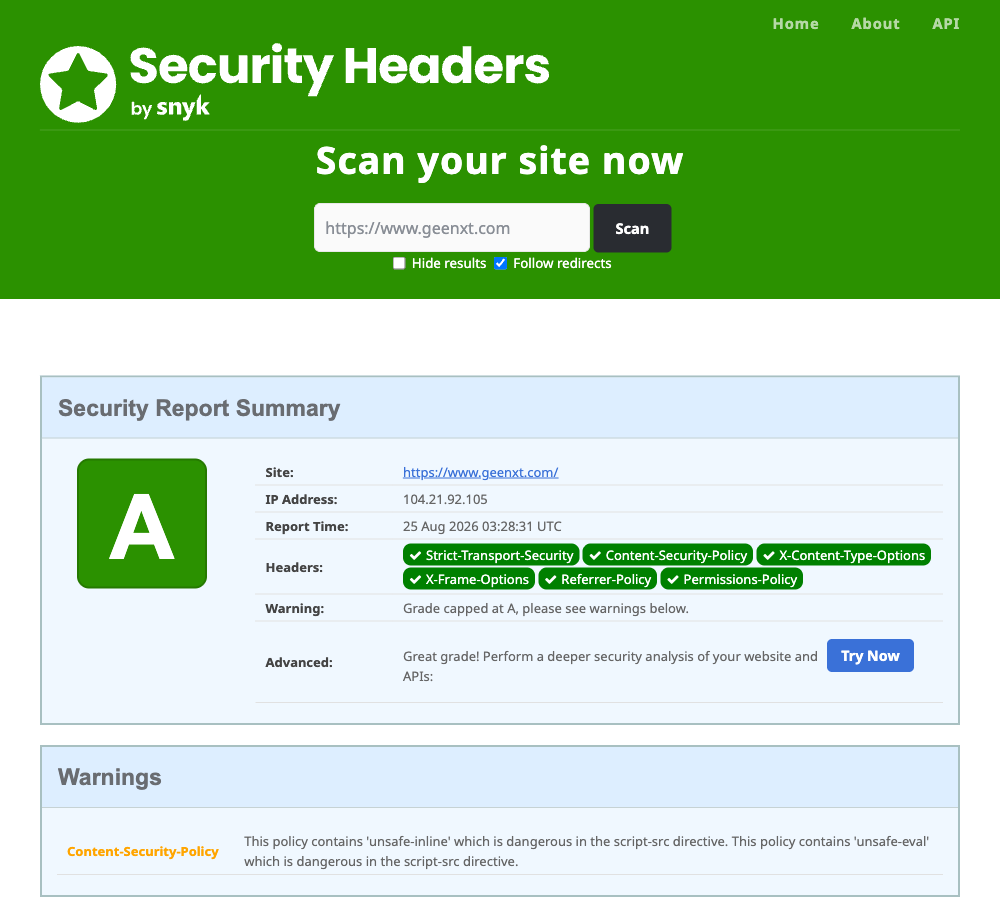
Add HTTP security headers in WordPress with HSTS, CSP, Apache .htaccess, Nginx, plugin-based options, validation steps, and rollout safeguards.
A practical WordPress compliance guide for cookie banners, consent tools, CCPA differences, Google Consent Mode v2, script blocking, audit checks, and policy alignment.
A practical threat reference for website owners covering the most common website security threats, how they happen, and the first mitigations to prioritize.